

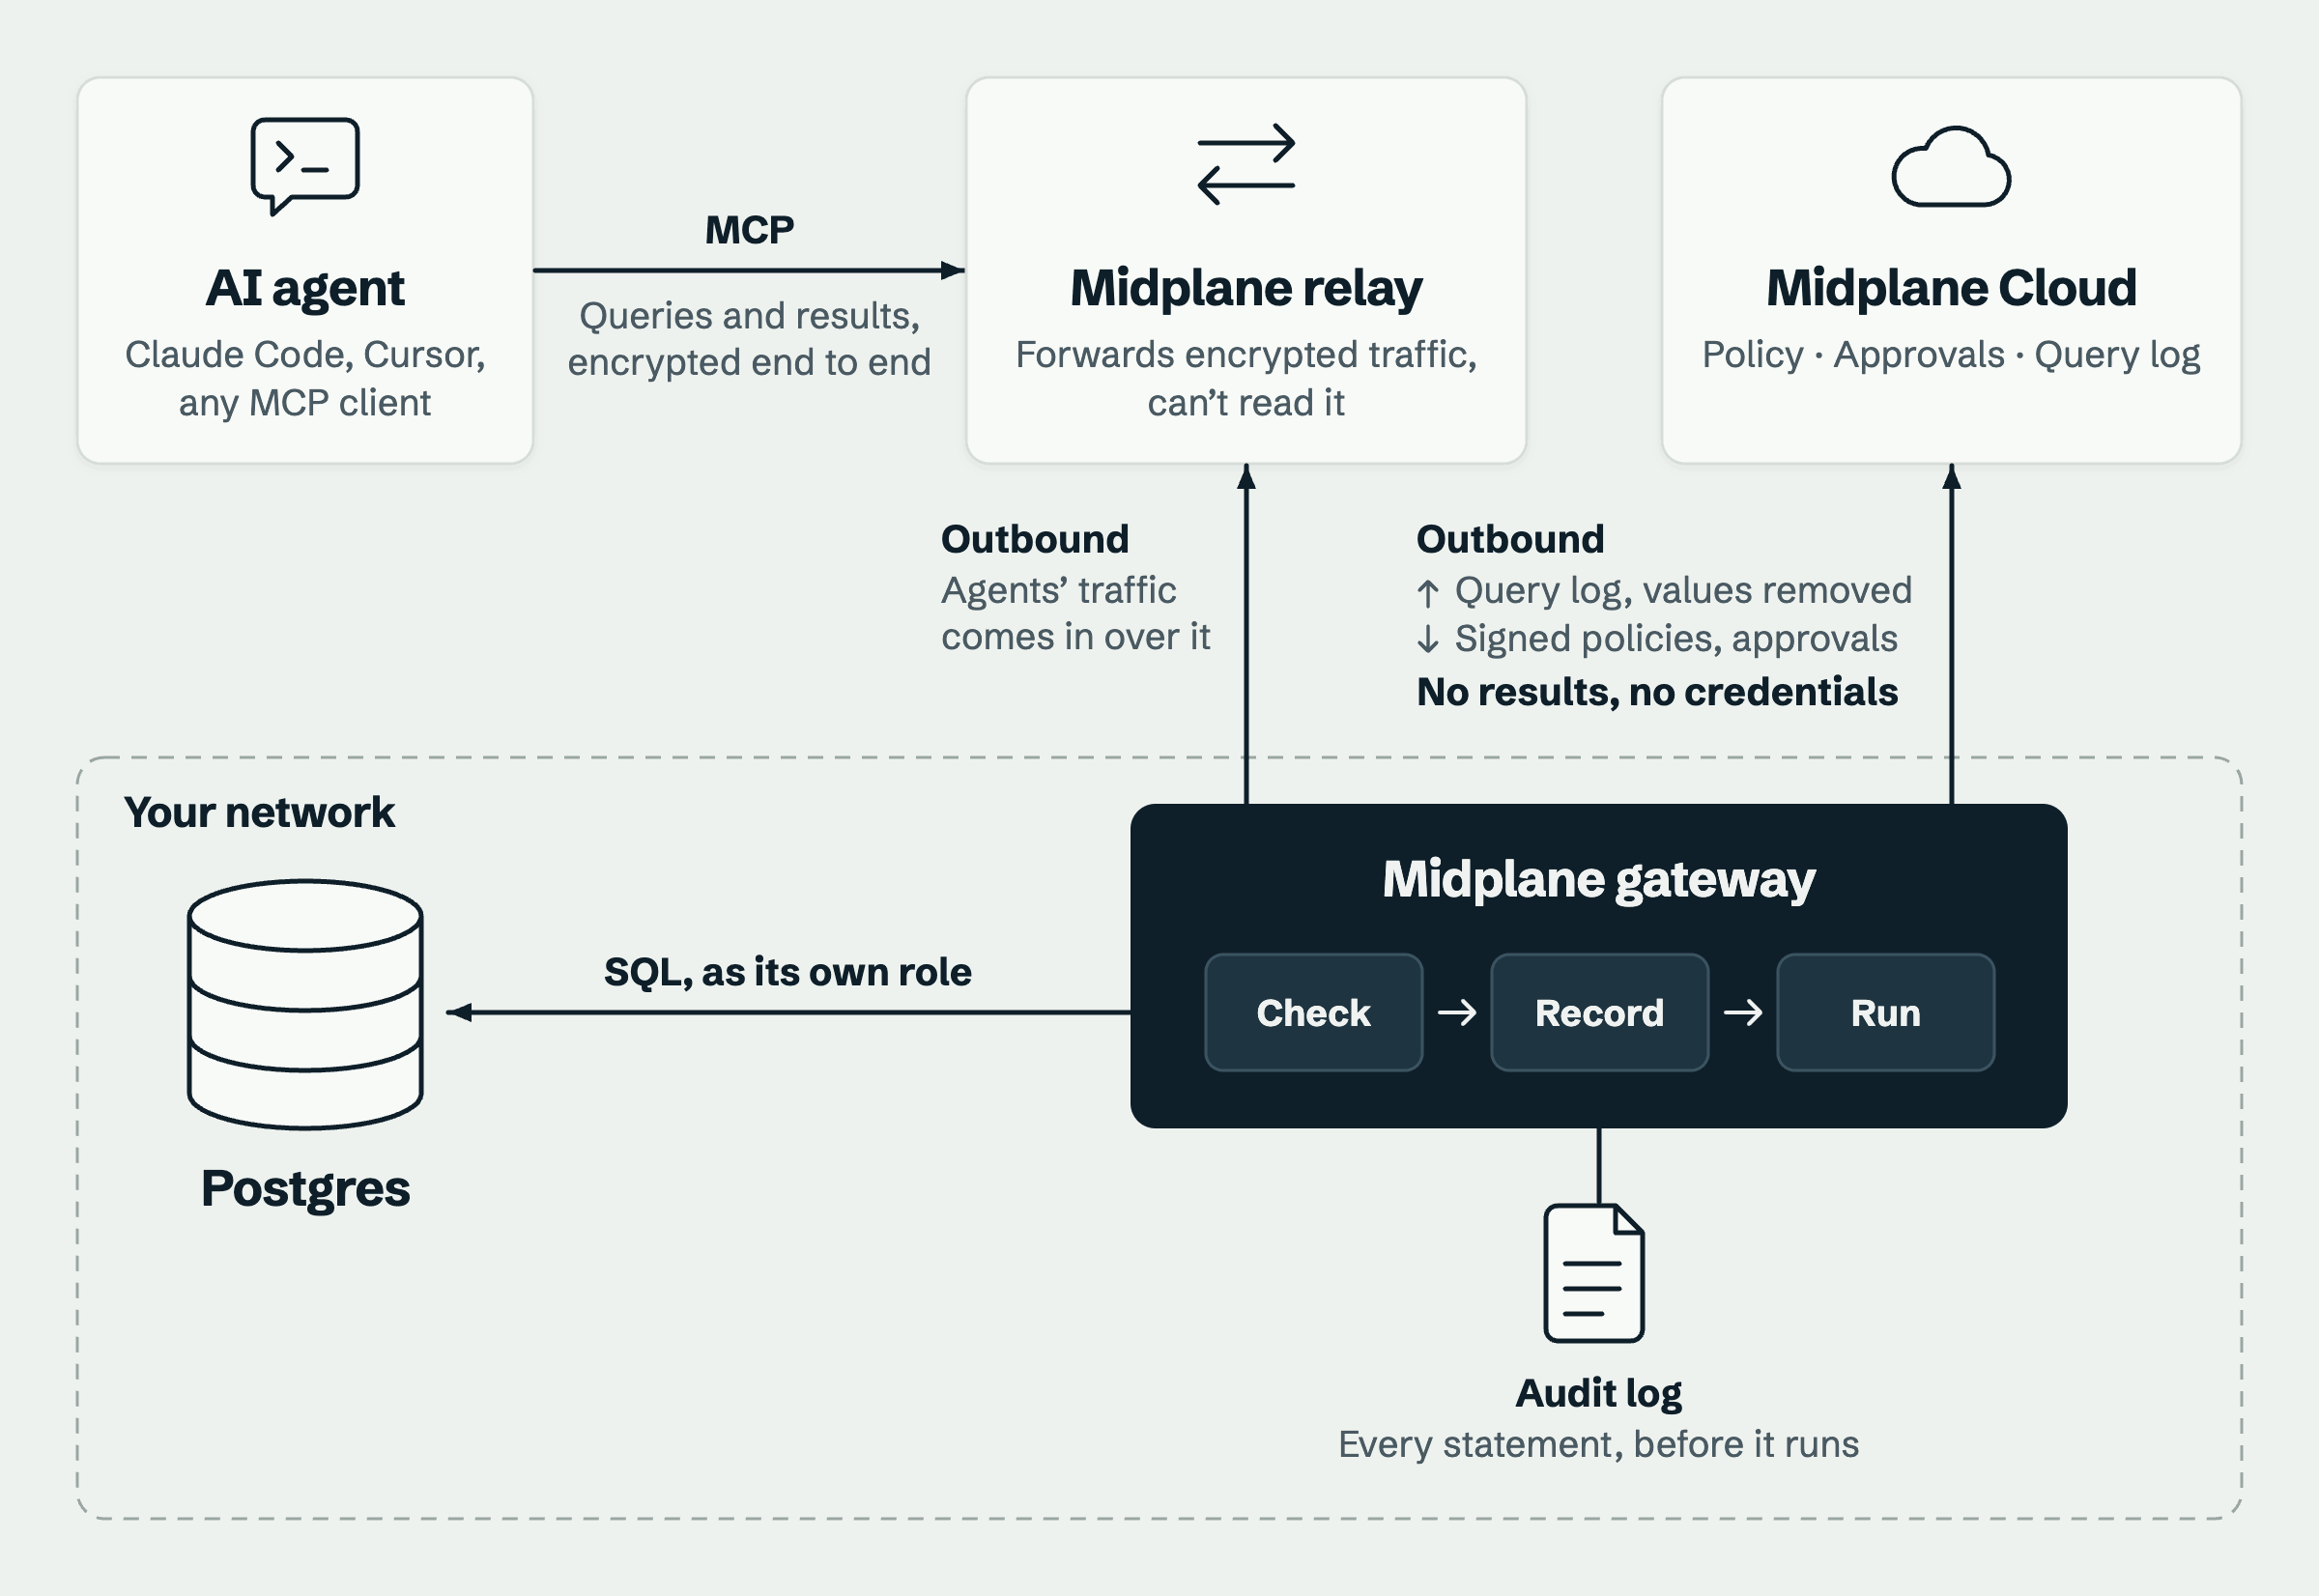
The parts
Gateway
One process in your network, next to your databases. It holds their
connection strings, checks every statement, and keeps the audit log.
Agents talk only to it.
Databases
Each has an id, such as
shop, and its own policy: which tables agents may
use, and what comes back masked.Agents
MCP clients such as Claude Code or claude.ai. Each signs in through the
gateway, and you choose which databases it may use.
Relay
Midplane’s, in its region. It gives a gateway in a private network a
public HTTPS URL, its Midplane URL, and passes agents’ encrypted traffic
to it without reading it.
Midplane Cloud
Where you write the policy, approve held writes and read the Query log. It
signs every policy it sends, and gets no rows and no connection strings.
Project
In Midplane Cloud: databases, their policies, their gateways and the agents
allowed in. Published policies reach every gateway in seconds.
How agents reach the gateway
Hosted agents, such as claude.ai and ChatGPT, run on their vendor’s servers,
so they need a public HTTPS URL. Behind the relay the gateway has one, even in
a private network with nothing open.
Through the relay
1
The gateway connects out
It keeps 4 connections open to the relay of its region, such as
relay.eu.midplane.app, and authenticates them with the token it uses
with Midplane Cloud.2
An agent connects to the Midplane URL
The URL’s name, such as
gw-7hq2m4xd.eu.midplane.app, points at the
relay. Each gateway gets its own when it joins a project.3
The relay passes the bytes on
It reads only the name the agent asks for in its TLS handshake, then
passes the still-encrypted bytes over one of that gateway’s connections.
4
TLS ends at the gateway
With a certificate the gateway got from Let’s Encrypt, for a key that
never leaves its disk. The agent’s statement then takes the path below.
The path of a statement
1
Check
The gateway parses the statement and checks it against the database’s
policy.
2
Record
It writes the attempt and the decision to its audit log, before anything
runs.
3
Run
An allowed statement runs, with masks applied inside the query. A held
write waits for a person’s approval.
What stays and what goes up
Stays in your network
Connection strings, database error messages, the mask salt, and the full
audit log. Results go only to your agents.
Goes to Midplane Cloud
Table and column names, statements with their values replaced, gateway and
database status, and writes held for approval, as written. Full statements
only if you turn them on.
Passes through the relay
Agents’ traffic, still encrypted. The relay sees the gateway’s name, the
addresses, and when and how many bytes cross, never what they say.